A recent cyberattack on refrigeration system left supermarkets across Europe with substantial losses. Belgium’s cybersecurity authority says warnings issued before the attacks helped limit the damage, but one expert argues that the incidents could have been prevented altogether.
The attack happened overnight from Sunday 1 November to Monday 2 November, and affected dozens of supermarkets across Belgium.
Three weeks before, on 13 October, the Centre for Cybersecurity Belgium (CCB) had issued a clear warning that some refrigeration systems in the country were vulnerable, following a previous attack in France on 12 October.
In its advice, the CCB explained that the vulnerability lies partly in how some refrigeration systems are connected to the internet, giving technicians the ability to monitor temperatures and control equipment from afar, without visiting the store.
Some older controllers, however, run on outdated software and can be accessed directly through the internet, without proper protection. The CCB sent an immediate warning to release security patches.
On 16 October, more than two weeks before the incident in Belgium, cybersecurity company Approach Cyber also identified approximately 700 refrigeration controllers in the country exposed to a security lapse, and easily accessible through the internet. Of those, around 400 appeared to be running vulnerable software, according to findings reported by specialist retail publication Gondola and subsequently by Le Soir.
The software involved in the French hacking incident was supplied by Danish manufacturer Danfoss, which said that the affected equipment was obsolete and no longer received software or security updates.
In Belgium, the exact technical cause of Monday’s incident has yet to be independently established, and it remains unclear whether the affected supermarkets were operating the same vulnerable systems identified by researchers.
Now, the CCB confirmed it had also sent targeted warnings to organisations' operating systems with similar vulnerabilities.
“We scan systems and can identify those presenting the same characteristics, which means we absolutely have to warn them about the risks,” Michele Rignanese, a CCB spokesperson, told The Brussels Times.
CCB is adamant that the warnings had helped reduce the number of businesses affected by Monday’s attack. “We received feedback yesterday, showing that these warnings helped limit the impact of the attack,” Rignanese said. "Many people told us that without these warnings, many more supermarkets would have been affected.”
Could the attacks have been prevented?
Hackers exploited this security system's Achilles' heel and manipulated temperature settings. They also activated defrosting functions, which resulted in a considerable amount of produce left to waste. How the hackers accessed this system is yet to be investigated.
The hacking affected around 40 Delhaize stores, alongside Carrefour, Intermarché and Spar supermarkets, as well as other businesses in Belgium, including butcher’s shops and an Ikea store in the city of Mons.
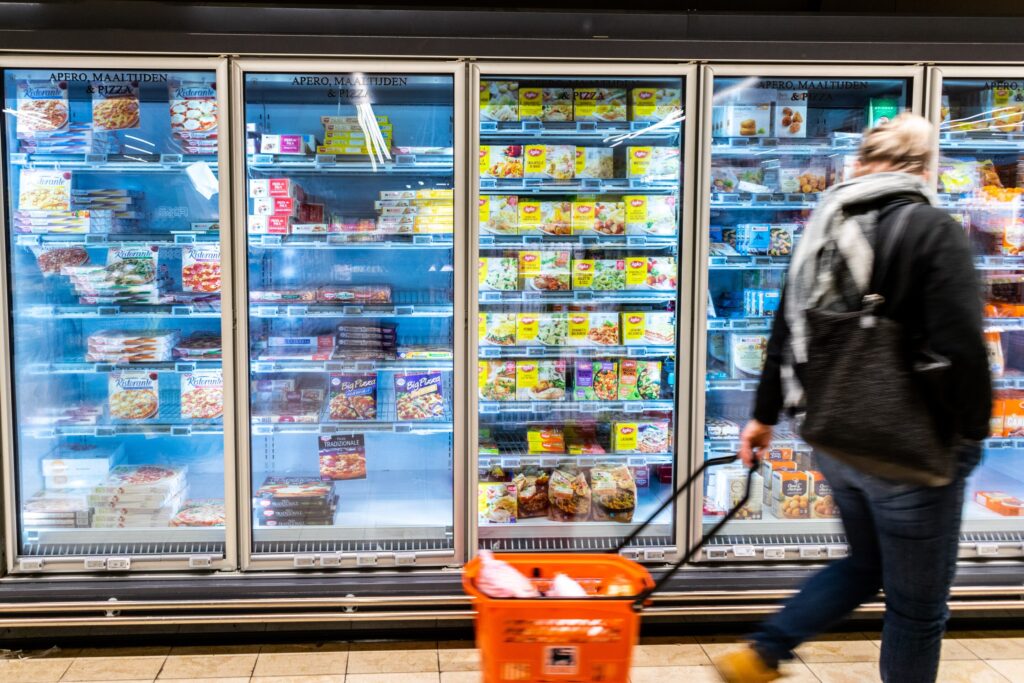
At the Delhaize supermarket in Arbre Ballon in Jette, the entire stock of frozen produce was spoiled. “We lost all our frozen goods. We’re talking about 60 metres of fridges,” a store manager told Sudinfo.
The shop's staff discovered the malfunction between 03:00 and 04:00 on Monday morning. “We had come in for something else. We saw that the fridges were breaking down and quickly realised it was a hack,” the store manager said. The total financial loss for Arbre Ballon in Jette is yet to be established.
Who is responsible?
Belgian cybersecurity expert Eddy Willems told The Brussels Times that the incidents were preventable; he argued that a relatively simple security measure, such as using a virtual private network (VPN) to restrict remote access, could have significantly reduced the risk.
“If they had done that, it would not have been a big problem as we have seen now,” Willems said.
However, the CCB warns zero risk does not exist. “At the very least, these systems should be blocked from direct internet access and additional security measures should be put in place,” CCB's Rignanese explained.
The question of responsibility is particularly important given that many Belgian supermarkets operate under franchise arrangements.
Willems said that this structure could complicate the implementation of cybersecurity measures: if a business is managed in a centralised manner, it becomes slightly more time-consuming for independently operated franchises to comply.
But the CCB puts the responsibility on the companies. “If they use systems that are not secure, they do so at their own risk."
Despite these attacks, Belgium is deemed well prepared to respond to cybersecurity threats, the CCB confirmed. Existing mechanisms already allow effective communication about incidents, including through European cooperation.
Businesses frequently overlook the cybersecurity implications of equipment connected to the internet, Willems warned. “We do that for our computers, we do that for our networks, but we forget about all the other systems which are connected to it."
Who is behind the attacks?
The identity of those responsible for the cyberattacks remains unknown to this day. Willems believes several scenarios are possible. No ransom demand had apparently been made, raising questions about the attackers’ motives.
One possibility, according to Willems, is that the incidents were carried out by amateur hackers experimenting with vulnerabilities in refrigeration systems.
The other scenario could be a state-sponsored activity. “There is a big possibility that this is driven by maybe Russia, maybe North Korea. We don’t know at this moment."
He suggested that Russian involvement could be consistent with attempts to intimidate European countries by demonstrating how easily everyday infrastructure can be disrupted. Willems also raised the possibility that state actors could recruit independent hackers to carry out attacks on their behalf.
However, he stressed that attributing cyberattacks to a particular country is extremely difficult during the early stages of an investigation.
The Belgian Federal Public Prosecutor's Office has opened an investigation, and is working to identify those responsible.
